Data allegedly from UMMC priced at $800K, posted on dark web
A data trove has been posted for sale on a dark web forum claiming to be from the University of Mississippi Medical Center (UMMC), which suffered a cyberattack in February that forced the closure of clinics and emergency services to operate on paper backups.
That incident, said to have occurred on Feb. 19, took over a week to resolve and was confirmed to involve the deployment of ransomware. UMMC has not confirmed whether sensitive patient data was accessed or taken by hackers, but a cybercrime cell is claiming that’s the case.
On the dark web, a prominent ransomware gang called Medusa is taking credit, posting on March 12 that it is in possession of data from UMMC’s network, said to be from throughout the health system.
The hackers are seeking an $800,000 payment, otherwise presumably they will sell the contents of the data trove to the highest bidder. A ticking clock on the post gave UMMC a time limit for a response, as is typical of the gang’s style.
The deadline is set for March 20.
Medusa’s posting, revealed by cybersecurity researchers at Comparitech, offers three options for the fate of UMMC’s data: Someone can pay $100,000 to extend the deadline, pay the $800,000 ransom to have it deleted, or offer the same amount to buy the information for themselves.
Screenshots accompany the post, offered as proof that Medusa has the goods. However, the contents are hard to decipher in the screenshot provided by Comparitech.
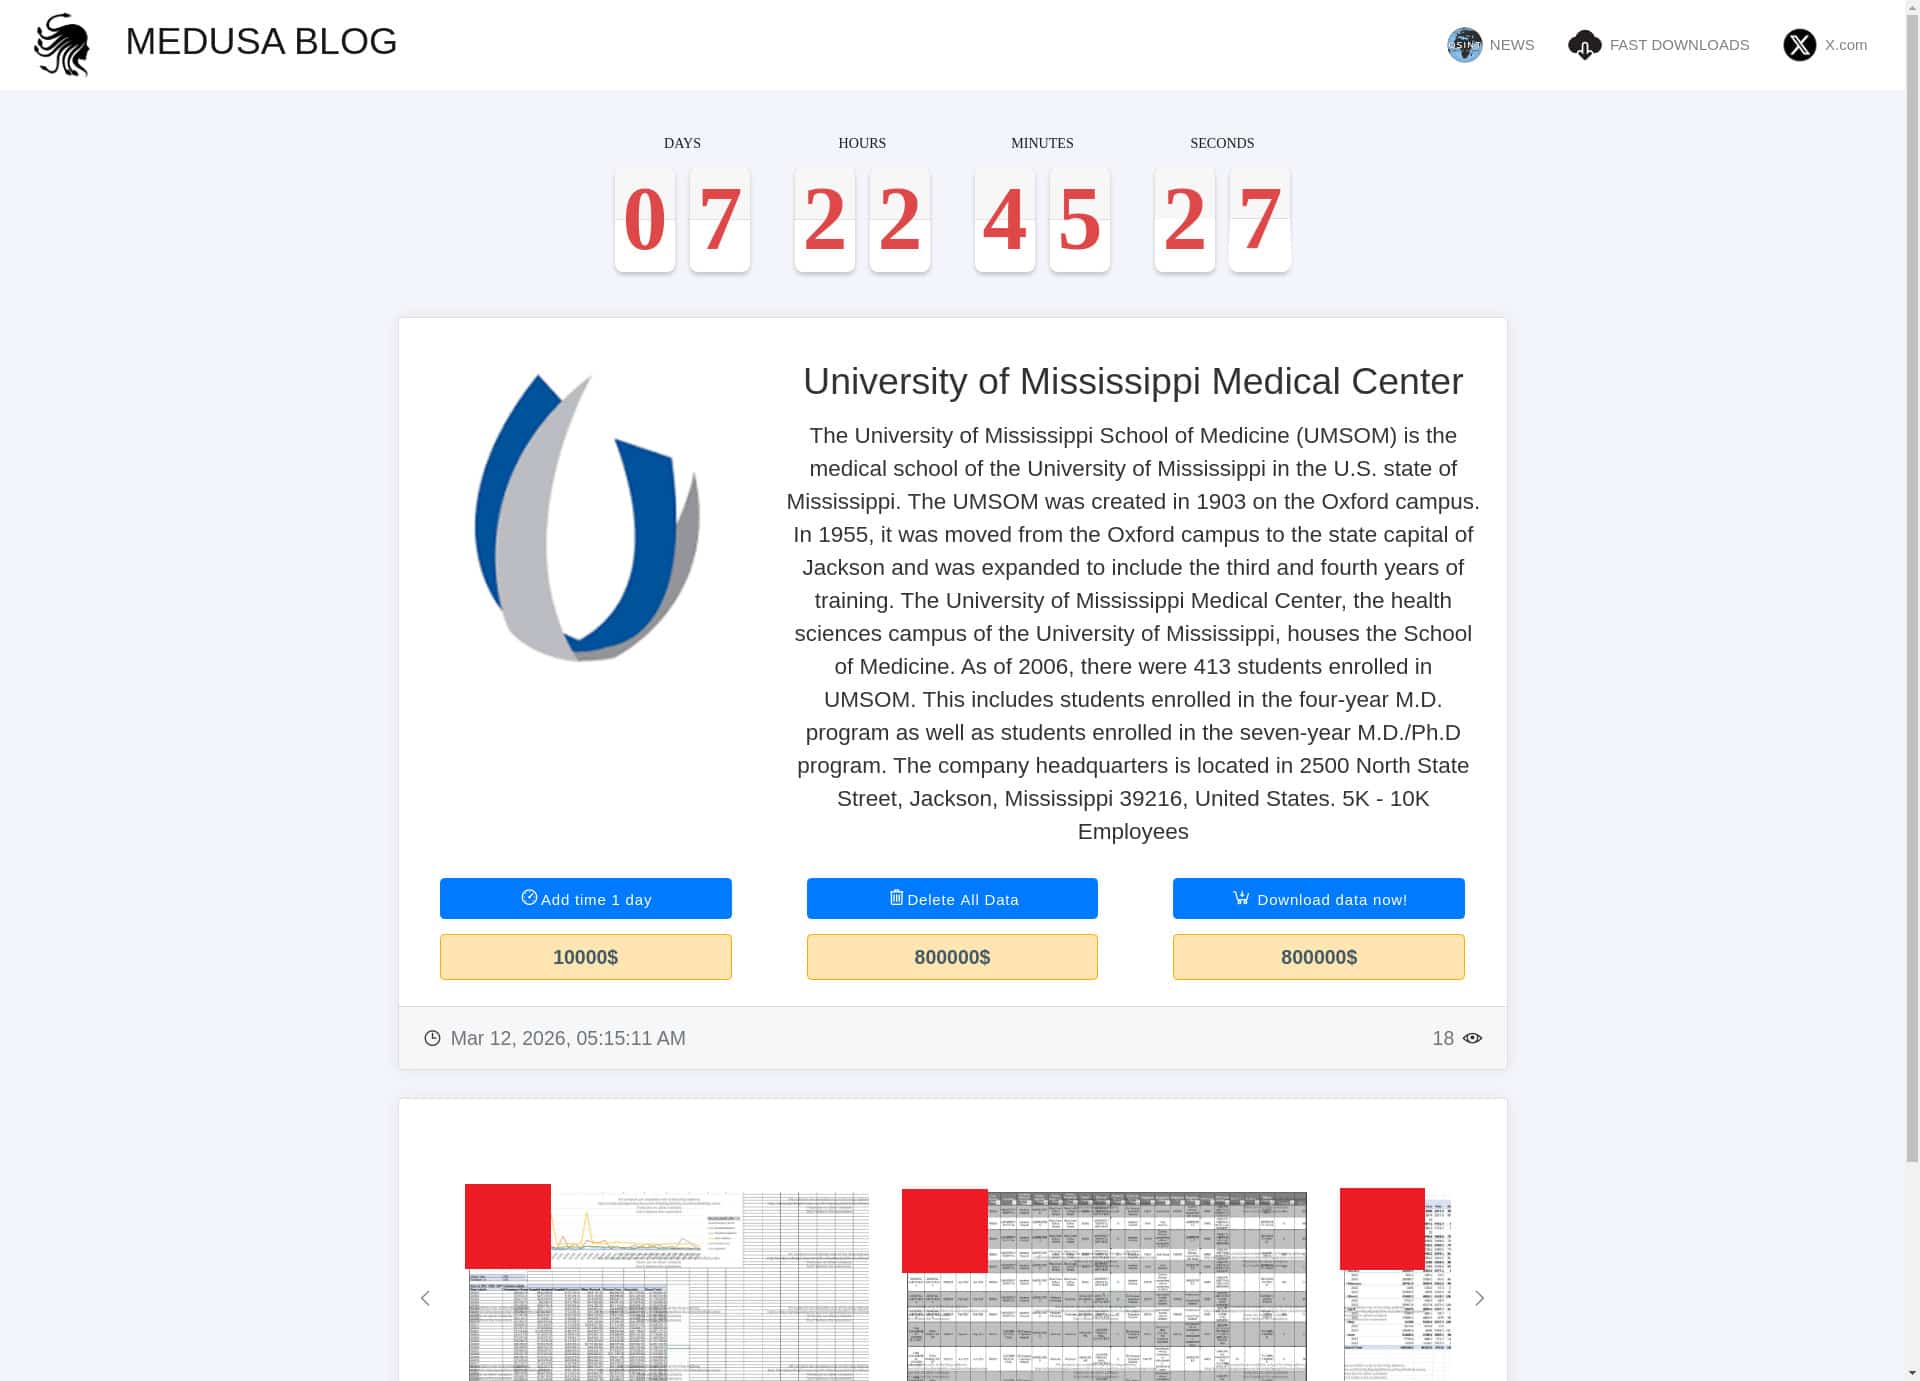
Typically, in these dark web advertisements, hackers will outline what information they stole as a teaser for buyers—but that does not appear to be the case here. Screenshots provided are of spreadsheets and charts that may contain sensitive information.
The size of files and scope of the potentially stolen information is unknown.
UMMC has not confirmed the legitimacy of the data trove. HealthExec previously reached out to the health system inquiring as to whether protected health information was accessed during the breach but did not receive a reply.
Medusa has been active since 2019 and has been responsible for numerous cyberattacks against healthcare, the public sector, and more. The identity of the gang members is unknown.
More than 200 breaches in two years
Dark Web Sonar, a website that attempts to track statistics on criminal activity associated with Tor, the network that makes the dark web possible, said Medusa has been responsible for 201 cyberattacks since 2024, all involving the deployment of ransomware.
The incidents span the globe.
This is the first data breach Medusa has claimed responsibility for in 2026, according to Dark Web Sonar’s tracking data.
Chad is an award-winning writer and editor with over 15 years of experience working in media. He has a decade-long professional background in healthcare, working as a writer and in public relations.